IT Forensics Services and Digital Investigations
MKS IT Forensics Services in Pakistan
As a system integrator, we provide IT forensics services that help businesses detect, analyse and resolve cyber incidents quickly. Our team investigates security breaches, recovers critical data and works alongside your existing IT infrastructure. Services range from threat detection and data breach analysis to collecting digital evidence for legal proceedings.
Our IT Forensics Services
Digital Evidence Collection and Preservation
Collecting and preserving digital evidence is the first step in any IT forensics case. Our team follows industry practice to capture evidence from affected systems, networks and devices without altering it, so it stays admissible in court. Every step is documented for a clear audit trail, which also helps businesses meet regulatory requirements.
Incident Response and Management
Our incident response service helps businesses deal with cyber threats quickly. We follow a structured process to identify, contain and resolve each incident, which limits downtime and damage to your IT infrastructure. The work covers threat detection and containment, recovery and forensic analysis afterwards, and it fits around your existing systems.
Malware and Ransomware Analysis
Malware and ransomware can disrupt operations and cause data loss. Our forensic specialists identify the type of attack, trace where it came from and assess the damage.
You receive a detailed report with practical steps to prevent repeat attacks and a recovery plan to keep downtime short. Our findings feed into your existing security setup to protect your network and sensitive data.
Data Recovery and Restoration
We recover lost or damaged data after cyber incidents or system failures, working with your existing IT setup to keep downtime to a minimum.
Network Forensics
We monitor and analyse network traffic to find security breaches and weak points as they happen, and report what we find so you can act on it.
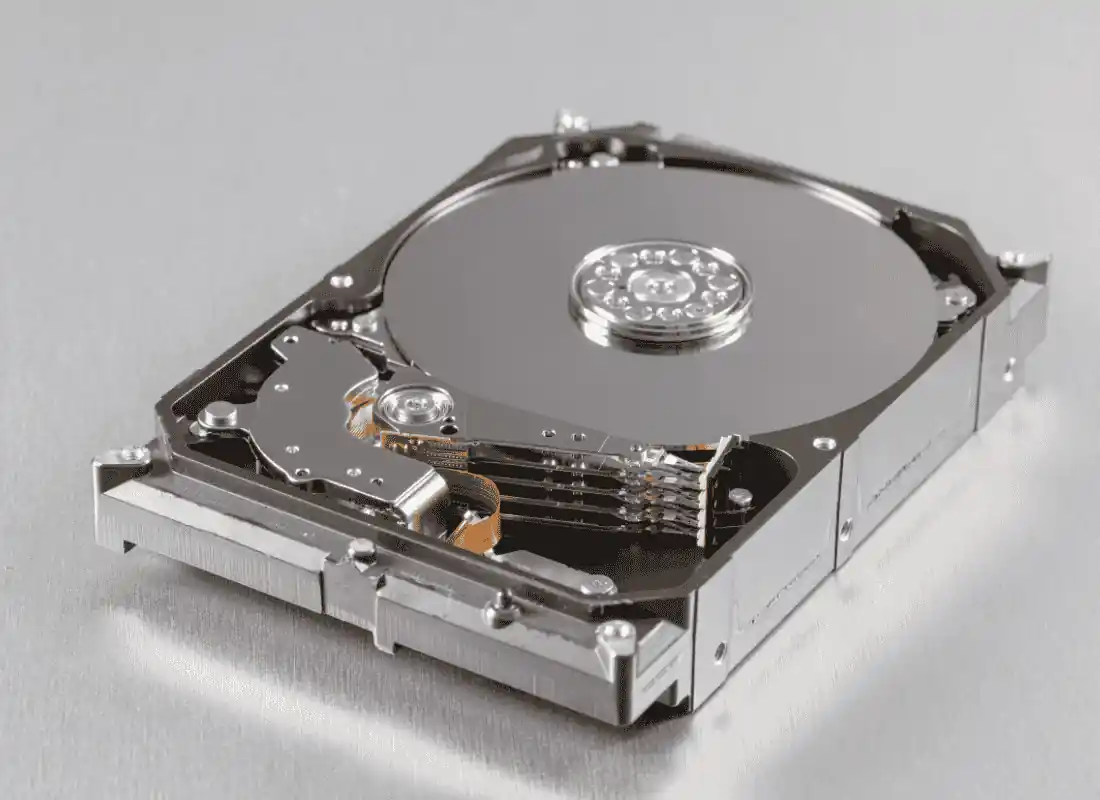
Disk and Memory Forensics
We extract and analyse data from hard drives and system memory to find evidence of cyber incidents, so malicious activity can be traced and dealt with.
Email and Communication Analysis
We investigate threats in your organisation’s email, messaging logs and collaboration platforms. Our analysts look for phishing attempts, insider threats and unauthorised access, which also supports regulatory compliance.
Our findings are linked to your existing IT setup to help protect sensitive information in your communication systems.
Forensic Reporting and Legal Compliance
Our forensic reports document all digital evidence in a form that meets legal standards. Each report sets out what we found and how the data was collected and analysed.
This documentation supports legal proceedings and regulatory compliance, and helps your organisation meet its legal obligations.
Cyber Threat Intelligence Integration
We bring threat intelligence into our analysis of system logs from different sources. This helps us spot unusual activity, track unauthorised access and review user behaviour across your IT infrastructure.
The result is a detailed audit trail that supports forensic investigations and incident response, and gives your organisation clearer accountability.
Log Analysis and Audit Trails
We review system activity logs to find possible breaches and keep detailed audit trails that support investigations and regulatory compliance.
Forensic Tools and Software
We supply forensic tools and software for collecting, analysing and preserving digital evidence, so investigations are thorough and evidence is ready for legal use.
Cloud Forensics
We investigate data held in cloud services, check cloud configurations, find unauthorised access and recover evidence to support incident response.